mgazelle.

Dr. Mongi Gazelle · Interim CIO · CTO · CISO

30+ years inside the rooms where technology, risk and people meet.

Interim CIO, CTO and CISO with mandates in banking, industrial manufacturing, retail and aviation — Sparda-Bank, ALDI Nord, GEA, Sennheiser. Programme and portfolio budgets of EUR 100M+, across 60 countries.

Available now for interim mandates, worldwide. Alongside the mandates I write the operating manuals working professionals need to come out of the AI shift on top — practical, role-specific, built from first-hand work.

  • 30+

    years of leadership

  • EUR 100M+

    programme and portfolio budgets

  • 60

    countries

  • 5

    languages

MIT CTO Certification

Ideas from the field

Latest from Mongi.

All articles →

A shorter take

One question I ask early in any engagement: how many AI tools are actually in use here? It is rare that anyone in the room can answer it. Often there is already a policy in its third draft, but no list. I think that order is backwards. A policy written before you know what is in use ends up either too abstract to apply or too strict to follow, and people quietly route around it. What has worked better for me is a plain inventory, built in two or three weeks. Every AI tool or feature in use, what data goes into it, who owns it and who approved it. The assistant add-ons in the office suite count. So do browser plugins, and the model a SaaS vendor switched on in last month's release. The list is almost always longer than the board expects. But it turns a vague governance debate into four or five concrete decisions: what to block, what to license properly, where personal or customer data must not go, and who approves new tools from now on. The policy can then be written around real cases, and the EU AI Act classification becomes work on known systems instead of guesswork. The harder part is keeping that list current once it exists. How do you handle it? #AIGovernance #CIO #EUAIAct

Read this note →

A shorter take

When I was CISO at a regulated bank, the most useful meeting of the month was not with the security team. It was thirty minutes with the board, going through the open audit findings one by one. Who owns it, what is the date, what is blocking it. No slides about the threat landscape. Just the list. With NIS2 now in force in Germany, management boards carry personal responsibility for cyber risk, and many are asking what that means in practice. In my experience it means exactly that meeting: a short list, named owners, real dates, and a board that asks why something slipped. The companies that struggle are rarely the ones without tools. They are the ones where nobody outside IT has ever seen the list. Does your board see the open findings, or a traffic light? #NIS2 #CISO #Governance

Read this note →
All notes →

Selected experience

The work behind the perspective.

Career highlights across banking, industry and retail. Different organisations; the same need for clear decisions and accountable leadership.

Sparda-Bank Berlin

Leadership in a regulated environment

CISO of a BaFin-regulated bank, with accountability for cybersecurity and regulatory delivery.

GEA Group

Security at an international scale

Global IT security programme leadership, including ISO 27001 certification for an organisation of 20,000+ users.

ALDI Nord

Connecting architecture and business

Head of enterprise architecture, bringing technology decisions into an international business context.

30+ years · 60 countries · 5 languages

Where the work was done.

Employers and interim mandates as listed in the CV, the client engagements delivered during ten years at Microsoft Germany, and earlier engagements across Europe and the Middle East.

Employers & interim mandates

  • Emirates Group logoEmirates Group
  • Sennheiser logoSennheiser
  • Sparda-Bank Berlin logoSparda-Bank Berlin
  • ALDI Nord logoALDI Nord
  • GEA Group logoGEA Group
  • Finanz Informatik Solutions Plus logoFinanz Informatik Solutions Plus
  • Microsoft logoMicrosoft

Client engagements

  • Deutsche Telekom logoDeutsche Telekom
  • Swisscom logoSwisscom
  • KPN logoKPN
  • Etisalat logoEtisalat
  • Deutsche Post logoDeutsche Post
  • DHL logoDHL
  • TNT logoTNT
  • Deutsche Bank logoDeutsche Bank
  • VHV Versicherung logoVHV Versicherung
  • Swiss Re logoSwiss Re
  • Munich Re logoMunich Re
  • Lufthansa logoLufthansa
  • Austrian Airlines logoAustrian Airlines
  • Mercedes-Benz logoMercedes-Benz
  • Volkswagen Group logoVolkswagen Group
  • Bundesagentur für Arbeit logoBundesagentur für Arbeit
  • Bundespolizei logoBundespolizei
  • BDBelastingdienst
  • Axel Springer logoAxel Springer
  • Sweco logoSweco

Earlier engagements & references

  • Adobe logoAdobe
  • IBM logoIBM
  • Etihad Airways logoEtihad Airways
  • SABIC logoSABIC
  • EDEKA logoEDEKA
  • PBPostbank
  • Apleona logoApleona
  • Evo Payments logoEvo Payments
  • VW Financial Services logoVW Financial Services
  • UWV logoUWV
  • UMCG logoUMCG
  • Carlson Wagonlit logoCarlson Wagonlit
  • Swiss (Swissair) logoSwiss (Swissair)
  • ADNOC (ADGAS) logoADNOC (ADGAS)
  • Qatargas logoQatargas
  • Dubai Internet City logoDubai Internet City
  • SOSaudi Oger
  • Saudi American Bank logoSaudi American Bank
  • ILSILS Jeddah
  • Commerzbank logoCommerzbank
  • Sparkasse logoSparkasse
  • RGRasGas
  • SSheraton

References on request

About · Dr. Mongi Gazelle

30+ years of leadership inside the rooms most people only read about.

Now I’m writing what I learned, in the language people doing the actual work can use on a Tuesday morning.

Dr. Mongi Gazelle

Dr. Mongi Gazelle

Interim CIO · CTO · CISO · Doctorate in AI & Digital Transformation Leadership

I’m Mongi — interim CIO, CTO and CISO, based in Rüthen, Germany, and available worldwide. I take on IT and security accountability where it is vacant, overloaded or under regulatory pressure, and hand it back to the line organisation in a governed state.

Behind that are 30+ years of international leadership: CISO of a BaFin-regulated bank at Sparda-Bank Berlin, head of enterprise architecture at ALDI Nord, global IT security programme lead at GEA Group — ISO 27001 certification with 100% audit success for 20,000+ users — and IT director at Sennheiser. Most recently I led group cybersecurity and application protection at Emirates Group in Dubai. Before that, ten years at Microsoft Germany on client programmes for Deutsche Telekom, Deutsche Bank, Lufthansa, Volkswagen and others.

In every one of those rooms, the same conversation comes up: what does this actually mean for the people doing the work?

The honest answer — the one most decks won’t print — is that AI is rewriting job descriptions quarter by quarter. I’ve watched which roles get cut, which roles get amplified, which workflows automate, which become more human.

That’s why this site exists. Every guide here is the operating manual I would hand the professional on the other side of the board decisions I’ve sat through for 30+ years.

Not theory. Not conference talk-track. The actions that work on a Tuesday, in your industry, in your role.

  • EUR 100M+programme and portfolio budgets
  • 100 %critical audit findings closed in a BaFin-regulated bank
  • MIT CTO Certificationplus Doctorate in AI & Digital Transformation Leadership (Kennedy University, USA)
  • NIS2 · DORA · BaFin/BAIT · ISO 27001regulatory delivery
  • DE · FR · AR · EN · NLGerman, French, Arabic native · English, Dutch business fluent

Direct line

Tell me what you’re building, what you’re worried about, or what you need solved this quarter.

An interim mandate, press, speaking, team licences or a question on a guide — every message lands in my inbox. I’m the one who replies, usually within two working days.

  • Reply window

    Two working days

  • Languages

    DE · FR · AR · EN · NL

  • Best for

    Boards · CIOs · founders

  • I never share

    Your name, your message

01 · The Flagship

The flagship guide · pre-order open

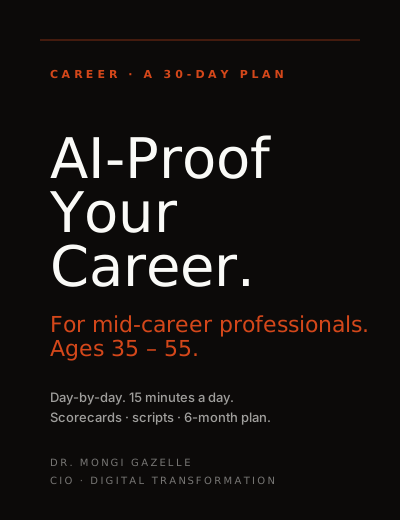
Cover: The 30-Day AI-Proof Career Plan

The 30-Day AI-Proof Career Plan

For mid-career professionals 35–55

A day-by-day plan to make yourself the person who runs the AI — not the one it replaces.

  • 65 pages, fillable PDF
  • Day-by-day, 15 minutes per day
  • Role-specific scorecards
  • Three scripts for the manager conversation
  • 6-month resilience template
  • EN at launch · FR shortly after
Read full details
Launch €39 · pre-order save €20· 14-day money back· EU VAT included

02 · Operating principles

Four rules every guide on this site is held to.

  1. 01

    Written from inside the room

    Every guide is built on first-hand work — the kind of work the buyer is preparing to face. Not a course built on top of a course.

    Rule 01
  2. 02

    Specific over inspirational

    Day-by-day actions, named workflows, real prompts, measurable outcomes. If a line cannot survive the Tuesday-morning test, it does not ship.

    Rule 02
  3. 03

    Returnable for any reason

    14-day no-questions money back on every guide and every subscription. If the work has not paid back inside two weeks, the refund is automatic.

    Rule 03
  4. 04

    Confidentiality first

    Written by a former bank CISO with 30+ years of international leadership. No tracking, no remarketing, no profile sold on. We hold only what the order needs.

    Rule 04

The Catalog

Every guide on mgazelle.eu.

1 available · 5 on the schedule

Coming next

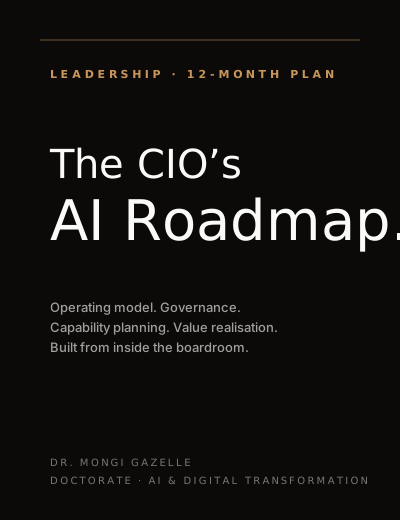
Cover: The CIO’s AI Roadmap
Coming
Leadership
The CIO’s AI Roadmap

A 12-month operating plan, from the inside

Operating model, governance, capability planning, value realisation. The agenda decomposed for the next quarter.

110 pages · PDF · 14-day refund

€49

€99

Notify me

Need a guide on a specific role? Subscribe and reply with the role — every reply is read.

From the desk of Dr. Mongi Gazelle

“AI doesn’t replace people. It replaces the version of you that hasn’t yet learned to operate it. These guides are the operating manual I would hand my best friend at 47, written from inside the rooms where the decisions are actually made.”
Dr. Mongi Gazelle·Doctorate in AI & Digital Transformation Leadership · Kennedy University

03 · The Boardroom Library

One subscription.Every guide I write.

Two new guides every month, drawn directly from work I am doing inside the boardroom — operating models, governance frameworks, cyber-resilience playbooks, AI-readiness diagnostics. The library opens with the second release.

€19/mo

Monthly · cancel anytime

€179/yr

Yearly · save €49

Notify me when the Library opens →

Founders' pricing held for the first 100 subscribers. Lifetime access (€499) opens at the same time.

  • Every guide on mgazelle.eu — current and future, no exceptions
  • Two new guides per month, drawn from active interim-mandate work
  • Monthly office-hours session with Dr. Mongi Gazelle
  • Member-only Slack for working through the playbooks together
  • EU VAT included · cancel anytime · 14-day money back

The AI Risk Brief

Understand the shift.Decide what to do next.

One email per month. Five minutes to read. Drawn from work inside boardrooms across Europe and the Middle East. New subscribers receive the free Layoff-Proofing Self-Assessment immediately — ten questions, no card.

  • 01 · A change in AI and what it means for working professionals.
  • 02 · A leadership perspective on the risk behind the headlines.
  • 03 · A practical question to bring to your next team conversation.
Explore my writing before subscribing →

Subscribe — free

Get the next AI Risk Brief.

No tracking pixels · unsubscribe in one click.